Tag Archives: IPSEC
Cisco ASA VPN Spoke to Spoke communication in 8.3 and later
This configuration was in ASA 8.4
Spoke to spoke communication has always been super easy in ASA Site to Site VPNs. As long as your CRYPTO ACL has the remote subnets in it, and NO-NAT Statements are there everything pretty much works.
The other day I had an issue getting it to work. After some research I was still struggling. All of my remote sites were in my Crypto ACL, my VPN was up and working to the hub, and any subnet behind the hub would work, but access to other IPSEC tunnels connected behind were not working. See rough sketch of the network below.

I checked Nat statements, looked great, but my traffic was not flowing. I decided to debug via ASDM this is the error I received.

Routing failed to locate next hop for ICMP then my outside (Louisville), and inside (Italy) address.
Other examples are:
Routing failed to locate next hop for TCP then my outside (Louisville), and inside (Italy) address.
Routing failed to locate next hop for UDP then my outside (Louisville), and inside (Italy) address.
Well, 192.168.17.0/24 does not live inside my firewall – it should be connected to the outside (US-Signal) VIA the VPN. Boom, that’s when it clicked. My nat statement is wrong, well not wrong, just missing. Since these connections are connecting to my outside network, and then going to my outside network – I need to create the nat statement with the source interface and destination interface being US-Signal.
A few things to note about the below statement – I put it at the top of my manual nat entries, and notice the interface – both are US-Signal my outside interface.
object network Louisville-Subnet
subnet 10.26.0.0 255.255.0.0
object network Italy-Subnet
subnet 192.168.17.0 255.255.255.0
nat (US-Signal,US-Signal) source static Louisville-Subnet Louisville-Subnet destination static Italy-Subnet Italy-Subnet no-proxy-arp route-lookup
As soon as I added this statement everything worked great. All of my spoke to spoke communication flowed through the hub perfectly.
Creating a Fortianalyzer to Fortigate IPSEC Secure connection
The Fortianalyzer is a great product. It can give very deep analysis of exactly what is going through the network and allow you to create/schedule reports to show this data. You also have very quick detailed monitoring at hand with the Fortiview. By default the Fortigates connect to the FAZ via SSL, all logs are encrypted. Recently, and I am not sure what the issue is, I have been having issues with certain FGTs connecting to the FAZ via SSL (I think its a cert issue..but still checking). So, we have a different option, to use IPSEC to create a tunnel and allow everything to be encrypted that way. This works great.
What we need to do
FAZ: add the device manually in the FAZ, enable “Security”, change the Local ID, Set the PSK.
FGT: Go in through CLI, disable SSL encryption, enable IPSEC, set the PSK.
So lets go to step one – adding the the device in the FAZ.
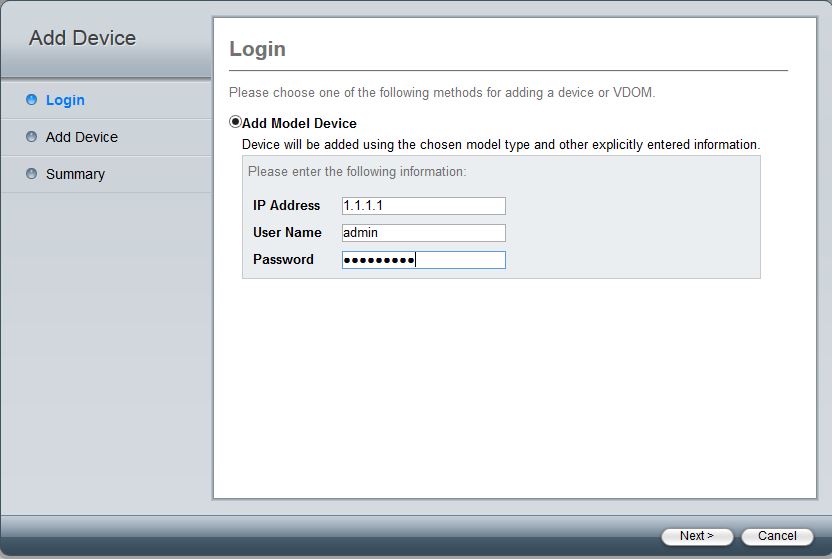
Log into the device, and select whatever Adom you want to add the FGT into. Then select to add a device, once this pops up fill in the needed info, you will need an admin account.
Select “Next” and fill in the needed info, you will need the S/N for this.
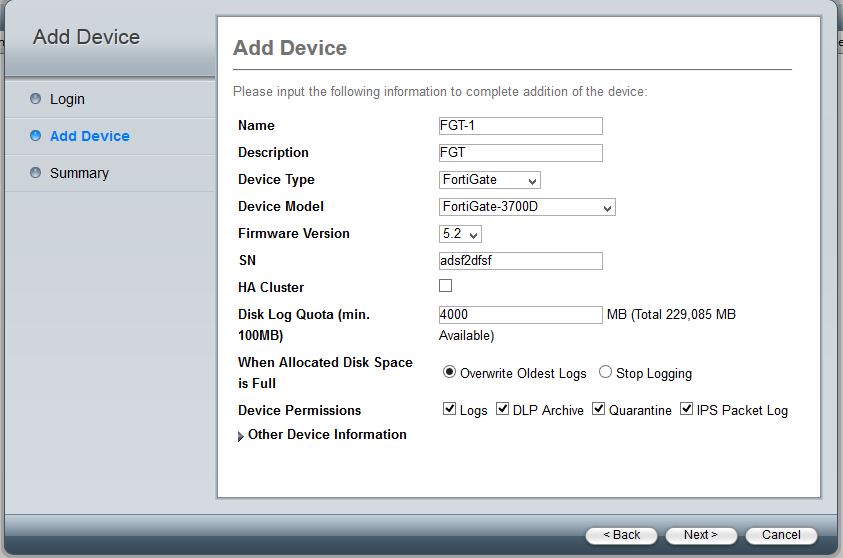
Once that is added you will be able to edit the device. Right click on the device name and select Edit.
From here you will need to enable IPSEC by checking “Secure Connection” and change the PSK. Notice Local ID this is what will identify the FGT. By default its the S/N but you can change it to anything. In this case I am using FGT1.

Now you should see something like this, notice that “Secure connection” is red.

Great, now its time for the device settings. I am going to do this through the CLI, its the only way to set the PSK as far as I know.
The commands are listed below. One thing to note is that once you select “Encrypt” you disable SSL and enable IPSEC.
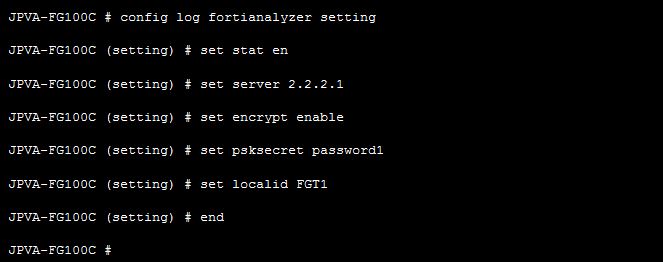
After all the commands are entered, you should be able to go to Log-Log Config-and test the connection to the FAZ. It should pop up that everything is working as listed below:
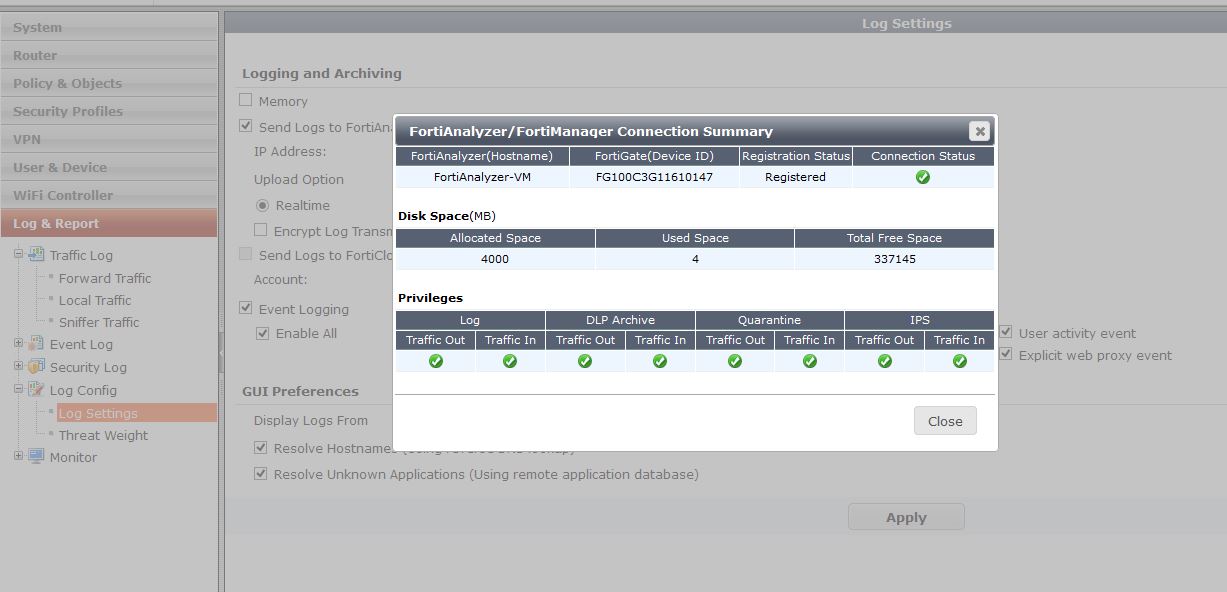
Lets check on the FAZ, to make sure everything looks correct.

Ok, this all looks great. That’s it, now we are using IPSEC to encrypt the logs. Its a good alternative to SSL if you find your self in the situation that the FGTs will not connect do to cert issues.
Cisco ASA IPSEC site to site VPN IOS 8.3+
There are multiple parts to the IPSEC SIte-to-Site VPN config.
– Create access list to specify what will be encrypted
– Create access list to specify what should go over the VPN, and not be natted
– Create Phase 1 (IKE) settings and apply it to the selected interface.
– Create our transformation set (what encryption settings we will use for phase 2).
– Create Phase 2 (ESP) settings otherwise known as a Crypto map.
– Apply Crypto map settings specifying interface.
– Create the tunnel object for peer.
Config:
ASA 1 Core
Create Objects
First create the objects representing what will be found on each side of the VPN.
config t
object network Local-Subnet
subnet 10.100.1.0 255.255.255.0
object network Remote-Subnet
subnet 10.100.2.0 255.255.255.0
Encryption Access-list
Next I will create the Access list to tell the firewall what to Encrypt
access-list VPN-to-Remote extended permit ip object Local-Subnet Remote-Subnet
Now we need to make sure traffic is not being forwarded out of our WAN interface, and that the firewall knows to send it over the VPN. We do this with a “No-Nat” statement. This is different than what it once was in 8.2 and below. We will specify this with a different kind of nat statement.
No NAT
nat (inside,outside) source static Local-Subnet Local-Subnet destination static Remote-Subnet Remote-Subnet
IKE Settings
Now its time for the VPN settings!
First lets create our IKE settings and enable it on the outside interface.
crypto ikev1 enable outside
crypto ikev1 policy 1
authentication pre-share
encryption 3des
hash sha
group 2
lifetime 86400
Create the IPSEC transformation
crypto ipsec ikev1 transform-set transfrom esp-3des esp-sha-hmac
Crypto MAP (Phase 2)
Now lets create our Crypto map and put it all together.
crypto map VPN 10 match address VPN-to-Remote
crypto map VPN 10 set pfs
crypto map VPN 10 set peer 1.1.1.2
crypto map VPN 10 set ikev1 transform-set transfrom
crypto map VPN 10 set security-association lifetime seconds 28800
crypto map VPN 10 set security-association lifetime kilobytes 4608000
There are a few optional settings like the lifetime, by default its 28800. In this config I am just making it known that’s what its set on. Also you can set “reverse-route” which will add the route to the remote subnet into the routing table. This way you can push it out in a routing protocol.
We will also need to apply the Crypto map to the interface.
crypto map VPN interface outside
Tunnel Group/PSK
Our last step is to create the tunnel group with our Peer IP/DNS name and set the PSK.
tunnel-group 1.1.1.2 type ipsec-l2l
tunnel-group 1.1.1.2 ipsec-attributes
ikev1 pre-shared-key presharedkey
Below is the config for the Remote side
config t
object network Local-Subnet
subnet 10.100.2.0 255.255.255.0
object network Core-Subnet
subnet 10.100.1.0 255.255.255.0
access-list VPN-to-Remote extended permit ip object Local-Subnet Core-Subnet
nat (inside,outside) source static Local-Subnet Local-Subnet destination static Core-Subnet Core-Subnet
crypto ipsec ikev1 transform-set transfrom esp-3des esp-sha-hmac
crypto ikev1 enable outside
crypto ikev1 policy 1
authentication pre-share
encryption 3des
hash sha
group 2
lifetime 86400
crypto map VPN 10 match address VPN-to-Core
crypto map VPN 10 set pfs
crypto map VPN 10 set peer 1.1.1.1
crypto map VPN 10 set ikev1 transform-set transfrom
crypto map VPN 10 set security-association lifetime seconds 28800
crypto map VPN 10 set security-association lifetime kilobytes 4608000
crypto map VPN interface outside
tunnel-group 1.1.1.1type ipsec-l2l
tunnel-group 1.1.1.1 ipsec-attributes
ikev1 pre-shared-key presharedkey

